BetMakers CoreDB API Authentication
The API is further secured using OAUTH2 client credentials grants. Each customer will be issued a client_id and a client_secret. See below for details below for details on how the clients integration application should obtain an access_token to use with the API.
OAUTH2
An app makes an HTTP POST request with a content-type of
application/x-www-form-urlencodedtooauth2_endpoint, and specifies the following parameters:grant_type– Set toclient_credentialsfor this grant type.scope– Set tographql/api
In order to indicate that the app is authorised to make the request, the
Authorizationheader for this request is set as “Basic BASE64(CLIENT_ID:CLIENT_SECRET)“, where BASE64(CLIENT_ID:CLIENT_SECRET) is the base64 representation of theclient_idand theclient_secret, concatenated with a colon.The authorisation server returns a JSON object with the following keys:
access_token– A validaccess_token.expires_in– The length of time (in seconds) that the provided access token is valid for.token_type– Set toBearer.
The customers application may re-use the access_token until it expires. For maximum performance it is recommended the token is re-used.
GraphQL endpoint
You will have been issued an api_endpoint. All GraphQL api requests should go to <api_endpoint>/query and be sent with an Authorization header containing Bearer: <access_token>. For more information...
GraphQL: A query language for APIs.
Our implementation supports GET and POST methods.
We also use support WebSockets for pushing data via GraphQL's subscriptions. See apollographql/subscriptions-transport-ws
In this case, the token should be embedded in the GQL_CONNECTION_INIT payload...
{
  "Authorization": "Bearer <access_token>"
}
GraphQL playground
Our UAT api_endpoint supports an interactive UI which also gives access to the docs and schema:
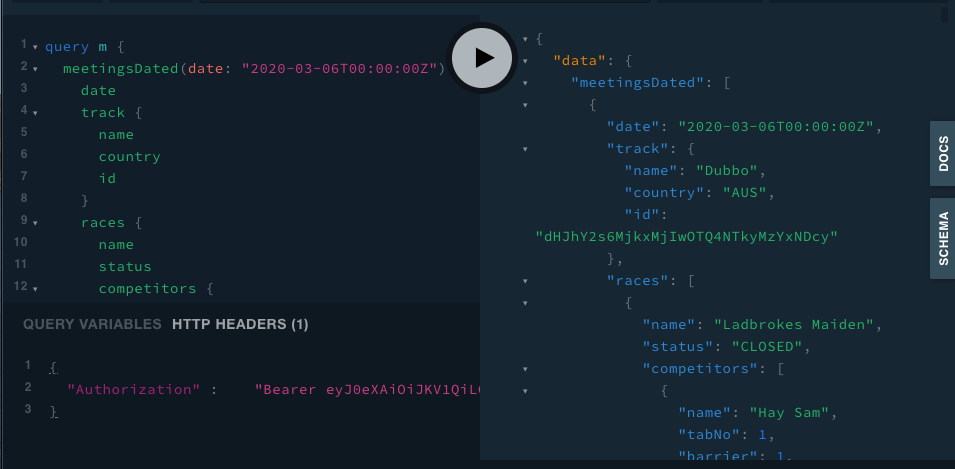
Just open the api_endpoint URL directly in a browser. Queries will only work once authenticated, so you'll need to open up the HTTP HEADERS tab at the bottom of the window and copy in some token details...
{
  "Authorization": "Bearer DEMO-ALL"
}
We have created a test access_token that never expires to allow exploration of the API, DEMO-ALL (this only works in UAT)
Parameters required for the customer to access
client_id- the OAUTH2 client identifier for the clients integration applicationclient_secret- the OAUTH2 shared secret for the clients integration applicationoauth2_endpoint- the URL that the application should use to exchange the client authentication details for anaccess_tokenapi_endpoint- the URL that the application should use to access the API
Refresh Tokens
Currently there is no token refresh mechanism available. For further information please visit the official docs.
Auth Troubleshooting
For any issues that arise when obtaining a token from the oauth2_endpoint please visit the official cognito docs.